
Compliance work has to be provable after the fact. ComplyWise keeps a permanent record of what happened in your workspace, who did it, and when, so an auditor's question is answered by the log rather than by memory.
What gets logged
- Document activity: uploads, new versions, renames, archives, deletions, and restores.
- Review decisions: every pass, flag, and comment on a document check, with the reviewer and timestamp.
- Screenings: each risk screening run and its result, plus every clearance decision made on a hit. Results and clearances are stored as an append-only history, so a re-screen never overwrites what an earlier run found.
- External link access: on share links, the invitation email and its outcome, every one-time code sent, every successful verification, every page open, and every individual document viewed or downloaded; on collection links, opens and uploads. All are recorded with time, connection details, and the address the visitor verified as.
- E-sign events: the full ceremony trail per envelope, opens, consent, each signature, declines, and link reissues, with the signer's connection details. Completed envelopes get a certificate document summarising this evidence.
- Administration: member invitations, role assignments, settings changes, and workspace-level actions like provisioning and renames.
Where to look
- The entity audit trail: each KYB record carries its own history, so you can answer "who uploaded this and who approved it" without leaving the document.
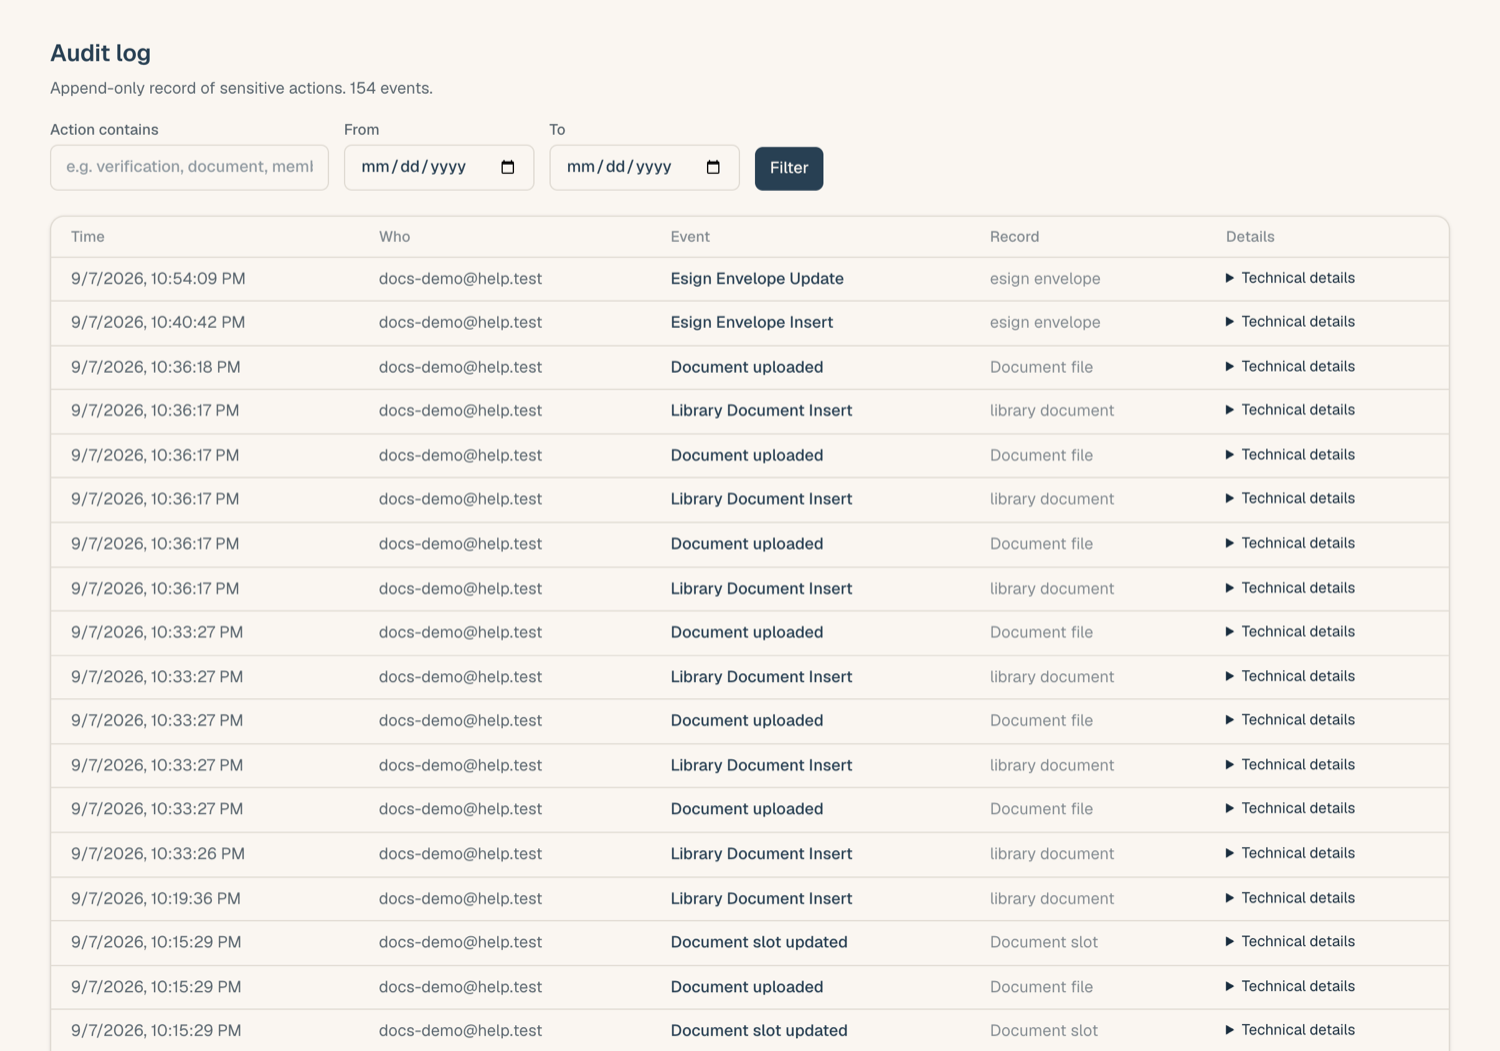
- The workspace audit log: the consolidated log across the workspace, available to members whose role grants audit access (Workspace Admins by default).
Why logs are append-only
Audit entries can be added but never edited or removed, by anyone, at any role. Deleting a document doesn't delete its history; the deletion itself becomes another entry. This is deliberate: a log that can be rewritten proves nothing, and regulators and banks treat tamper-evident records as the baseline. It also protects your team, because an honest mistake plus its correction is a defensible story, and both halves stay on record.
What this means day to day
Work normally. You don't switch anything on, and you can't switch it off: logging is a property of the platform, not a setting. If you ever need an extract of the record for an auditor, contact support@complywise.io.
Related articles
- External links: share, collect, and sign: how link access is controlled and logged
- Workspace settings: legal hold and retention controls
- Invite and manage members: roles and who can read the audit log